Ethereum clients patch flaw that could redirect ETH rewards

 Prefer us on Google


Ethereum client developers Teku and Besu have released security updates to address a certificate vulnerability that could allow attackers to impersonate services used by validators and potentially redirect their block rewards.
Summary
- Ethereum clients Teku and Besu have released security updates after a certificate vulnerability was found that could allow attackers to redirect validator block rewards to their own addresses.
- The vulnerability originated from weak cryptographic keys associated with eight certificate authorities operated by Indian company eMudhra, which could allow attackers to create fraudulent certificates.
- Teku warned that attackers could impersonate external services used by Ethereum validators and manipulate block proposals or obtain sensitive validator signatures under certain configurations.
- Default Teku mainnet configurations were not affected, and developers confirmed that no exploitation of the vulnerability had been reported.
- Operators using standalone Teku or Besu installations must update their Java environments separately, as the latest Docker image fixes do not automatically update locally installed Java certificates.
According to security advisories accompanying the releases, the issue originated from compromised certificate authority keys belonging to Indian digital certificate provider eMudhra, which left certain Ethereum node configurations exposed to forged HTTPS connections.
Teku released version 26.10.3 on October 27, while Besu introduced version 26.10.2 a day earlier. Both updates remove trust for affected eMudhra certificates from their Docker images, which operators use to deploy and run Ethereum node software.
The vulnerability could affect validators that rely on external services for signing transactions, communicating with beacon nodes or receiving block-building information. An attacker would need to intercept an affected connection and present a forged certificate that the validator's software accepts as legitimate.
Teku's developers confirmed that default mainnet configurations were not affected and said there had been no reported exploitation of the vulnerability.
Ethereum security flaw traced to compromised eMudhra certificates
The security issue began with a cryptographic error involving eight intermediate certificate authorities operated by eMudhra, whose private keys were found to have been generated using insufficient randomness.
Researchers identified the problem on October 17, discovering that the private keys could be mathematically recovered from information available in the public certificates.
According to an October 26 security advisory from Microsoft, six of the affected certificates were used for securing internet connections, while the remaining two were associated with code signing.
The compromised keys could allow someone to create certificates that appeared genuine to applications that continued trusting the affected certificate authorities.
eMudhra revoked the affected intermediate certificates on October 18, while technology providers began removing trust for the compromised certificate chains from their software.
Microsoft subsequently blocked the affected certificate authorities through a Windows security update on October 20 and released another update on October 26 to remove seven associated certificates from its trusted list.
However, the problem remained relevant to Ethereum because Teku and Besu use Java, whose certificate validation does not check revocation status by default.
As a result, affected Java installations could continue accepting certificates associated with the compromised authorities even after their revocation.
How attackers could redirect Ethereum validator rewards
Teku's security advisory identified several possible attack scenarios involving validators that communicate with external services through HTTPS connections.
One scenario involves an attacker impersonating a remote beacon node used by a validator to coordinate its duties on Ethereum.
If the attacker successfully intercepted the connection and presented a forged certificate, the validator could receive manipulated information about the block it was preparing to propose.
According to Teku, such an attack could cause a validator to propose a block that directs transaction fees to an address controlled by the attacker.
The advisory identified external signing services as another potentially exposed component. These services hold validator signing keys separately from the main node software and provide signatures when requested.
An attacker impersonating an external signer could potentially obtain signatures associated with validator exits, depending on the configuration and available protections.
Teku classified this scenario as particularly serious, although configurations using mutual TLS authentication could limit the consequences to a denial of service.
Other potentially affected connections include execution clients, block builders, relays and services used to retrieve validator configuration information.
The vulnerability did not affect Ethereum's underlying peer-to-peer networking protocols, which do not rely on the compromised certificate authorities.
Teku and Besu release fixes for affected Ethereum nodes
Following the disclosure, Teku released version 26.10.3 to remove four certificate roots from its Docker images, including emSign ECC Root CA G3, emSign Root CA G1, emSign Root CA G2 and AAA Certificate Services.
Besu introduced the same certificate removals in version 26.10.2, addressing the risk for operators using its updated Docker images.
However, the releases do not automatically update Java installations maintained separately by node operators.
Users running Teku or Besu through standalone binary distributions must check their installed Java runtime and update its trusted certificates where necessary.
Teku warned that operators still using Java 26 would need to migrate to Java 25 because the former version had reached end of life and would not receive the required patched build.
The advisory further identified certain testnet configurations as potentially exposed, including setups that download their initial blockchain state over HTTPS.
The security updates follow other recent concerns involving Ethereum validator infrastructure. Earlier this month, crypto.news reported that MetaMask had begun exiting affected validators following a separate infrastructure security incident disclosed on September 30.
More recently, Ethereum developers corrected a validator deposit flaw in the upcoming Glamsterdam upgrade after researchers identified a scenario where builder accounts could receive ETH intended for validators.
The Glamsterdam upgrade has separately faced delays after developers postponed its Hoodi testnet activation to investigate smart contract compatibility concerns involving EIP-8037.
The October 26 postponement removed the scheduled activation of both the Amsterdam execution changes and Gloas consensus changes, along with a proposed increase in Hoodi's gas limit to 200 million. Ethereum developers have not announced a replacement activation date.
-- Price
This content is provided for general informational purposes only and doesn't constitute financial, investment, legal, or tax advice. Any events, rewards, online promotions, or related information mentioned herein should not be considered a recommendation, solicitation, or invitation to purchase, sell, trade, or otherwise deal in any crypto assets. Crypto assets are highly volatile and may result in loss. The availability of WEEX services, products, and related events may vary by region. You are responsible for ensuring that your participation is in accordance with applicable local laws and regulations.
You may also like
Only 10% of FOMO app’s Solana wallets were profitable after fees
Stellar Launches Project Thruput for Fee-less Parallel Transactions
Stellar launches cross-chain messaging with ethereum through VIA Labs
Ethereum Researchers Explore Transaction Assertions to Reduce Signing Risks
Hyperliquid trader’s $170M oil orders raise spoofing concerns
ENSv2 launches on Ethereum as NFT claims require name upgrades
Omani Phaze Ventures Launches Two Investment Funds Targeting Over $75 Million
BNB Chain contract deployments nearly triple to 12.3M in Q3
Morgan Stanley Research on China's Robot Market: Companies Still Want Humanoid Robots, but Large-Scale Deployment Will Have to Wait

Coinbase and Thunes Tie Stablecoins to Local Bank and Wallet Payouts
Morgan Stanley Raises Global Electricity Growth Forecast: Who Will Share the $500 Billion Increment in the Power Market Beyond AI?
Ritual Raises $30 Million to Launch Token: AI Game Changer or Retail Investor Trap?
Can Derive V3 Maintain Its Leadership in the Growing On-Chain Options Market?
After a 95% Drop in TVL, Sony's L2 Soneium is Finally Launching Its Token
Onchain Fees: Crypto Protocols Earn $4 Billion in the Third Quarter
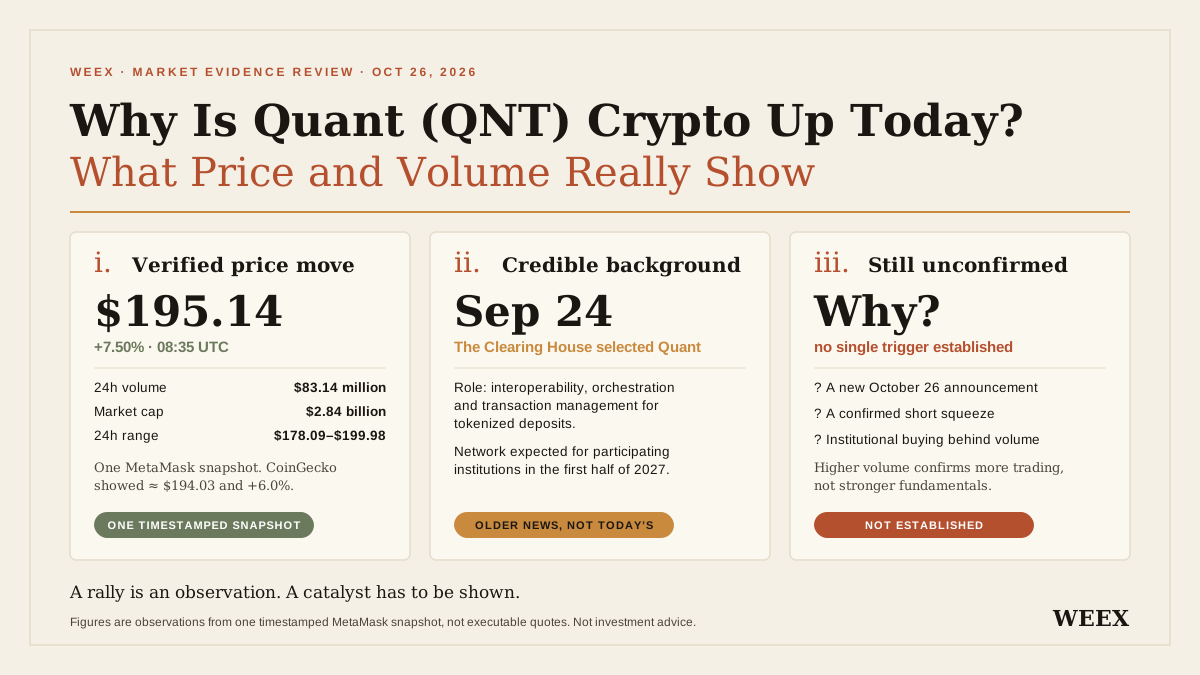
Why Is Quant (QNT) Crypto Up Today? What Price and Volume Really Show
Why is Quant (QNT) up today? Review price and volume evidence, the banking partnership timeline, token-demand assumptions, and risks before trading.
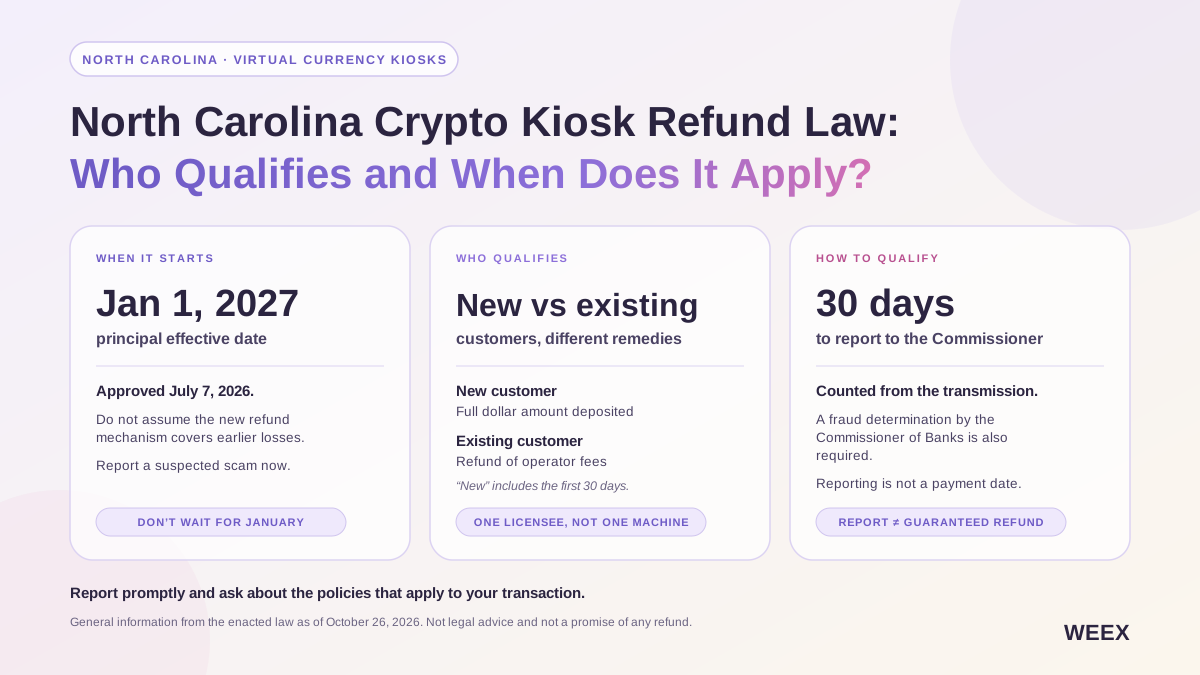
North Carolina Crypto Kiosk Refund Law: Who Qualifies and When Does It Apply?
Understand North Carolina’s crypto kiosk refund law: the January 2027 start date, who qualifies, reporting deadlines, and documents victims should keep.
AI Reduces Vulnerability Discovery Costs, Crypto Industry Divided in Response
Ethereum: Glamsterdam postponed after risks detected on 13 contracts
Who is Making Money from Digital Dollars? Profit Sharing Among Stablecoin Issuers, Distributors, and Payment Providers
[ETH Letter] Meritz Securities Reviews Tokenization of Korean Securities Based on OP Stack
Ethereum Releases CALLSTATUS Instruction EIP Draft
Paradigm Releases Audited Built-in JIT Compiled New EVM evm2
Weekly: $68,000 Theft from Ukrainian in Trust Wallet, Circle's Lawsuit Against Trump Over $2 Billion in UAE, and Historic Solana Update
Delay of the Glamsterdam Update on Ethereum Postpones Activation on Hoodi
Arbitrum Launches Developer Guild, Offchain Labs Becomes First Member
Hyperliquid L2 Elysium to Deploy Node at TheHUB in Tokyo
Heatbit's $899 Water Heater Element Mines Bitcoin While It Heats Your Tank
Ethereum Delays Test of Glamsterdam Update
Cryptocurrency Exchange Acknowledges Error After Reports of Millions in Losses
Only 10% of FOMO app’s Solana wallets were profitable after fees
Stellar Launches Project Thruput for Fee-less Parallel Transactions
Stellar launches cross-chain messaging with ethereum through VIA Labs
Ethereum Researchers Explore Transaction Assertions to Reduce Signing Risks
Hyperliquid trader’s $170M oil orders raise spoofing concerns
ENSv2 launches on Ethereum as NFT claims require name upgrades


